Cut Audit Prep: 6 Step Continuous Compliance Roadmap for Organizations
Practical 6 step roadmap pairing REM with targeted automation and template free extraction to cut audit prep and close evidence gaps.

The fastest way to reduce audit effort and make compliance operational is to adopt continuous compliance backed by targeted automation and a linked compliance management system. Organizations seeking compliance efficiency see faster audit prep, fewer control gaps, and measurable ROI once they stop treating audits as annual fire drills. Frameworks like SOC 2 and ISO 27001 already reward this shift, and platforms such as DocuPOW show what continuous evidence collection looks like in practice.
TL;DR:
- Automating continuous evidence collection can significantly reduce audit preparation time and detect control failures more quickly than traditional point-in-time reviews.
- Implementing automated controls requires building an obligation register and mapping processes before deploying monitoring tools to prevent automating the wrong controls.
- Focus on automating high-effort controls like access management and vulnerabilities first, since approximately 70% of controls are automatable with existing source systems.
- A well-designed compliance management system must link obligations, controls, owners, and evidence, with regular reporting, third-party risk monitoring, and remediation tracking.
- Using agent-based, template-free document extraction tools like DocuPOW addresses evidence collection bottlenecks, especially from unstandardized PDFs and vendor documents.
Table of Contents
- What Creates Compliance Inefficiency in the First Place?
- What Is Continuous Compliance and Why Does It Work Better?
- How Do You Actually Implement This? A Step-by-Step Roadmap
- Which Automation Categories Actually Move the Needle?
- What Does a Well-Designed Compliance Management System Look Like?
- What Mistakes Should You Avoid When Rolling This Out?
- How Does DocuPOW Fit Into This Roadmap?
- Author Perspective: Compliance as Infrastructure, Not Overhead
- Ready to Pilot Continuous Compliance? Start Here
- Sources
- FAQ
What Creates Compliance Inefficiency in the First Place?
Most compliance drag traces back to five recurring failure modes. If any of these sound familiar, the problem isn’t your team’s effort. It’s the operating model underneath it.
- Tool and data fragmentation: evidence lives across shared drives, email threads, and three different GRC tools that don’t talk to each other.
- Reactive evidence collection: teams scramble for six weeks before every audit instead of maintaining readiness year round.
- Control duplication and drift: the same control gets tested by three teams, while another control quietly stops working and nobody notices.
- Unclear ownership: a control exists on paper, but no single person is accountable when it fails.
- No continuous oversight: leadership sees a compliance dashboard once a quarter instead of tracking real-time metrics.
These aren’t isolated annoyances. They compound. A fragmented toolset makes ownership harder to assign, which makes drift harder to catch, which turns every audit into a sprint. Breaking that cycle is the entire point of moving to continuous compliance.
What Is Continuous Compliance and Why Does It Work Better?
Continuous compliance means monitoring controls and collecting evidence in real time, rather than reconstructing a compliance story once a year. Point-in-time audits ask “were you compliant on the day we checked?” Continuous compliance asks “are you compliant right now, and can you prove it in five minutes?” That distinction changes how teams work day to day.
Three shifts define the model:
- Evidence becomes continuous, not retroactive. Instead of pulling logs and screenshots the week before an audit, systems capture proof of control operation automatically, which reduces audit-prep time and friction because there’s nothing left to reconstruct.
- Monitoring replaces sampling. Auditors traditionally sample a handful of transactions from the year. Continuous monitoring watches every relevant control event, which auditors increasingly prefer because it closes the gap between “policy exists” and “control actually operated.”
- Frameworks adapt accordingly. SOC 2 and ISO 27001 audits now favor organizations that can produce a live evidence trail over those that produce a binder assembled the week before the auditor arrives.
The payoff shows up in hard numbers. Automating evidence collection and continuous monitoring can cut audit-prep hours dramatically while also shrinking the window where a failed control goes undetected. That’s the efficiency case in one sentence: less scrambling, fewer surprises, cleaner audits.
How Do You Actually Implement This? A Step-by-Step Roadmap
Continuous compliance isn’t a software purchase. It’s a sequence. Skip a step and the automation you bolt on later won’t have anything reliable to connect to.
- Build an obligation register. Map every regulatory and contractual obligation to the controls that satisfy it. Without this, automation just speeds up chaos.
- Prioritize with a risk-based lens. A Regulatory Efficiency Methodology approach, combining value-focused analysis with risk-based prioritization, has produced 20 to 35% cost reductions in pilot cases when paired with process mining.
- Map and mine your processes. Process mapping shows where evidence gets created; process mining shows where it gets stuck, duplicated, or lost in handoffs.
- Automate the highest-effort controls first. Access management and vulnerability controls tend to deliver the fastest ROI, and roughly 70% of controls are automatable where source systems and APIs already exist.
- Stand up dashboards and alerting. Continuous monitoring only pays off if someone sees the alert before the control fails, not after.
- Pilot, then measure. Track cycle time, percentage of controls automated, and cost per compliance activity, then expand what works.
Pro Tip: Run your pilot on one obligation, not one department. Picking a single regulatory obligation and automating it end to end gives you a clean before-and-after metric, whereas piloting an entire department mixes too many variables to prove anything.
Teams that follow this order rarely need to rip out their first automation investment. Teams that automate before mapping obligations usually do.
Which Automation Categories Actually Move the Needle?
Not every “compliance tech” purchase pays for itself. Five categories consistently do, based on where manual effort concentrates:
- Regulatory intelligence and horizon scanning: automated detection of rule changes so your obligation register updates itself instead of relying on someone reading newsletters.
- Continuous control monitoring: API-based connectors that pull evidence from source systems (identity providers, cloud infrastructure, HR systems) instead of asking a control owner to screenshot a setting.
- Template-free document extraction: AI that pulls structured data out of PDFs, scanned forms, and vendor contracts without a rigid template, which rescues evidence that would otherwise sit untouched in a shared drive.
- Process mining and workflow automation: tools that expose handoffs and rework in the compliance workflow itself, not just in the controls it monitors.
- A single data model for evidence: integration work that lets monitoring, extraction, and reporting tools reference the same obligation and control IDs, so evidence doesn’t fragment across systems again.
Consultancies estimate that technology-enabled compliance, when properly integrated and governed, can save 15 to 30% on compliance operating costs. The “properly integrated” qualifier matters more than the number. A best-of-breed approach connected by a common architecture tends to scale better than a single monolithic platform trying to do everything.
What Does a Well-Designed Compliance Management System Look Like?
A compliance management system holds up when four elements stay linked instead of living in separate spreadsheets: obligations, the controls that satisfy them, the owners accountable for each control, and the evidence proving the control ran. Break any one of those links and the system degrades into paperwork.
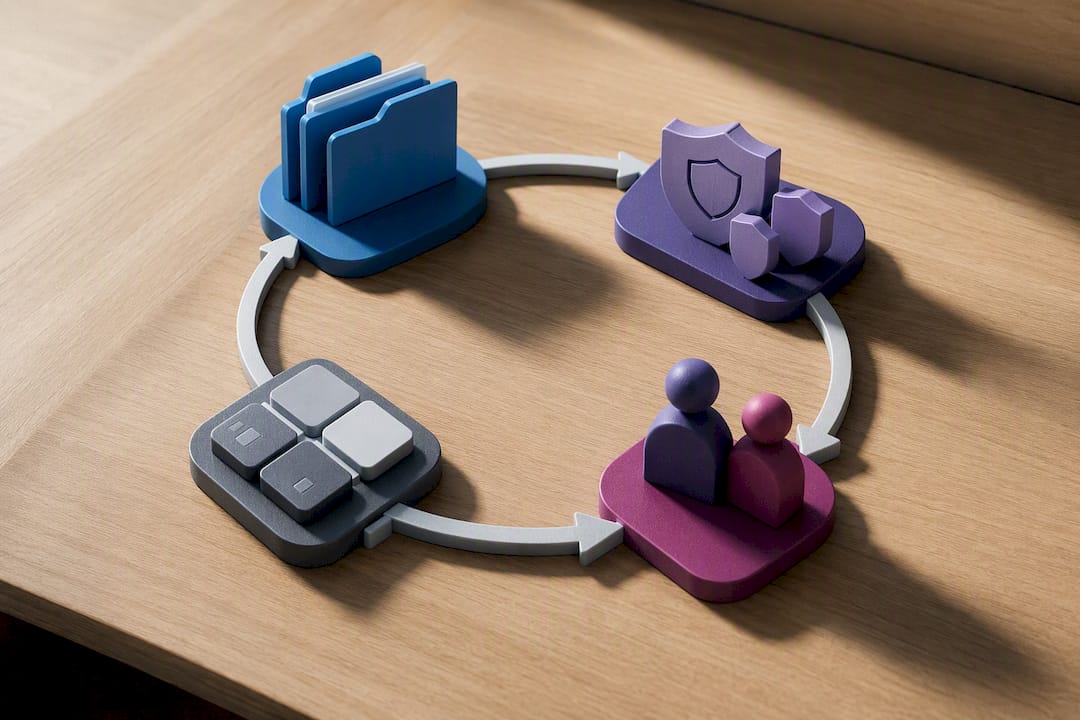
Regulators grade this directly. The OCC’s Comptroller’s Handbook on Compliance Management Systems expects board oversight, an active compliance program, and independent testing, not just a policy binder. Examiners increasingly ask whether controls are operating right now and whether evidence is available on demand, not whether a policy document exists somewhere.
A functioning CMS also needs:
- Defined reporting cadence to the board, not an annual summary buried in a risk committee packet.
- Third-party risk monitoring that treats vendor compliance evidence with the same rigor as internal controls.
- Remediation tracking that closes the loop when monitoring catches a gap, so the audit trail shows the fix, not just the failure.
Get these four links solid and automation has something real to plug into. Skip this step and you’ve automated a broken process faster.
What Mistakes Should You Avoid When Rolling This Out?
The biggest mistake is automating before mapping. Teams that buy monitoring tools before finishing the obligation register end up automating the wrong controls, or automating controls nobody owns.
A close second: building a new silo. If your continuous monitoring tool doesn’t feed the same CMS as everything else, you’ve just added a fourth fragmented data source to the three you already had.
Watch for these specific traps:
- Automating without obligation mapping first produces fast, confident answers to the wrong question.
- Standing up a parallel system instead of integrating into the existing CMS doubles your maintenance burden.
- Removing human review from high-risk decisions trades a slow process for a fast, unaccountable one.
- Rolling out to everyone at once instead of piloting on one obligation invites resistance and confused feedback.
Pro Tip: Define your KPIs before the pilot starts, not after. Teams that wait to decide what “success” means tend to declare victory on whatever metric happened to improve, which makes the second pilot much harder to sell to leadership.
Change management matters as much as the technology and automation. Communicate early wins in terms people outside compliance understand, cycle time and audit hours, and train users by role rather than running one generic session for the whole company. A structured approach to documentation helps standardize that training across teams.
How Does DocuPOW Fit Into This Roadmap?
The hardest part of continuous compliance is usually evidence, not monitoring. Most organizations already know which controls matter. What they lack is a fast, reliable way to pull evidence out of the PDFs, scanned forms, and vendor documents where it actually lives.
DocuPOW’s template-free extraction approach addresses that gap directly. Because it doesn’t rely on rigid document templates, it can pull structured data from invoices, contracts, and supplier documents even when formats vary, which matters when your evidence sources span dozens of vendors that will never standardize their paperwork. Human-in-the-loop review keeps a person validating anything flagged as unusual, so automation handles the routine extraction while judgment stays with your team on the exceptions.
Three pilot scopes tend to work well as a starting point:
- Automated invoice evidence for financial controls that currently require manual reconciliation.
- Regulatory submission packet assembly, pulling data from multiple source documents into one audit-ready file.
- Supplier document evidence, extracting terms and certifications from vendor contracts for third-party risk monitoring.
Each of these maps to a control category examiners already ask about, which makes the pilot easy to defend internally.
Author Perspective: Compliance as Infrastructure, Not Overhead
Compliance efficiency isn’t a cost-cutting exercise. It’s a speed problem. Every hour spent reconstructing evidence after the fact is an hour your team isn’t spending on the risk analysis that actually protects the organization. Treat compliance as operational infrastructure, and measure the pilot the same way you’d measure any infrastructure investment: cycle time and audit readiness, nothing softer. If you’re a leader reading this, the next step is small: authorize one pilot, assign one owner, set two KPIs. That’s it.
— Syed Naveed Abbas
Ready to Pilot Continuous Compliance? Start Here
DocuPOW gives compliance and operations teams a way to close the evidence gap without hiring a document-processing team. Its agent-based extraction reads any document layout, invoices, contracts, supplier certifications, without a template setup phase, and routes uncertain cases to human reviewers instead of guessing.
For a roadmap-aligned pilot, start with a single high-friction evidence source: invoice reconciliation, supplier contract terms, or a regulatory submission packet. Measure cycle time before and after, and let that number make the case for expansion. The platform overview walks through how extraction, workflow orchestration, and analytics connect for exactly this kind of use case, and the Automated Invoice Processing tool is a practical place to run a first test. Plans start at the Starter tier for $99 per month, with a Professional tier at $499 per month for teams running larger evidence volumes; Enterprise pricing is available on request through the same pricing page.
Sources
- Compliance Management Systems (Comptroller’s Handbook) — OCC
- Continuous Compliance: Today’s Ultimate Guide — Splunk
- Continuous compliance monitoring guide — Proveably
FAQ
What Are the Pillars of an Effective Compliance Program?
Common frameworks point to five pillars: leadership commitment, risk assessment, policies and controls, training and communication, and monitoring with enforcement. The OCC’s guidance on compliance management systems folds these into board oversight, an active program, and independent testing.
What Are the Three C’s of Compliance?
Definitions vary by industry, but a common version is Culture, Controls, and Communication, the idea that policies only work when the organizational culture reinforces them and communication keeps everyone aligned on what’s expected.
What Are the Top Global Compliance Concerns Right Now?
Data privacy, third-party and vendor risk, AI governance, cybersecurity resilience, and evolving ESG reporting requirements consistently top compliance leaders’ lists. Frameworks like the NIST AI Risk Management Framework have emerged specifically because AI governance wasn’t adequately covered by older compliance models.
How Is DocuPOW Different From a Standard OCR Tool?
DocuPOW uses agent-based, template-free extraction that adapts to new document layouts without manual setup, paired with human-in-the-loop review for anything flagged as uncertain. That combination targets the evidence-collection bottleneck that slows down most continuous compliance programs.
What Does DocuPOW Cost?
DocuPOW’s Starter plan runs $99 per month and the Professional plan runs $499 per month, both listed on the pricing page. Enterprise pricing is available on request through the same page.
Recommended
See DocuPOW on your documents.
Stop building templates. Start extracting data.